CI/CD Pipeline Security Services in the USA That Protect Every Software
Your CI/CD pipeline is the path every change takes from developer commit to production deployment. Attackers who compromise that path do not need to break your application they wait for your own pipeline to carry malicious code into production for them. CyberZEALS secures CI/CD pipelines across the USA so your software delivery process is as protected as the software it delivers.
980+
Successful Services
10+
Years of Experience
900+
Satisfied Clients
10+
Industries Served
Securing CI/CD Pipelines Starts by Understanding the Attack Surface
The CI/CD pipeline attack surface is larger than most organizations account for. It includes source control repositories, build runners, container registries, secrets stores, deployment infrastructure, and every third-party tool that has write access to any of those components. A compromised developer credential, a poisoned dependency, or an overprivileged build runner can introduce malicious code into a release without anyone reviewing it as code. Securing CI/CD pipelines requires treating every component in the delivery chain as a potential attack vector not just the application code itself.
Secure CI/CD Pipeline Consulting That Runs in Three Phases
Pipeline security that works in practice accounts for how your team actually delivers software the tools they use, the release cadence they maintain, and the organizational constraints that determine what can change and how fast. Our secure CI/CD pipeline consulting begins with that operational reality.
- Discovery and Pipeline Security Testing
Every repository runner secrets reference third-party integration and deployment target mapped and reviewed for the conditions that create pipeline compromise risk before any controls are designed or deployed.
- Architecture Design for Security in CI/CD Pipeline
SLSA-aligned pipeline architecture, zero-trust build infrastructure design, and a hardening roadmap with prioritized changes that reduce the highest-risk exposures first without requiring your engineering team to stop shipping while security gets implemented.
- Continuous Pipeline Security Service Monitoring
CI/CD events streamed to SIEM, anomaly detection configured for build behavior, and incident response procedures documented for the pipeline abuse scenarios most likely to affect your specific delivery environment.
Eight Controls That Create Security in CI/CD Pipelines From End to End
Each control addresses a specific compromise path. Applied together, they eliminate the conditions pipeline attackers rely on finding.
Access Governance Across the CI/CD Pipeline
SSO and MFA enforced on every pipeline tool, service account permissions scoped to exactly what each build job requires, and just-in-time elevation for administrative access so no credential in the pipeline holds persistent elevated rights.
Credential Management for Secure CI/CD
Centralized secrets manager with short-lived credentials issued via OIDC rather than stored environment variables, automated rotation on defined schedules, and pre-commit scanning that catches secrets before they reach the repository history.
Dependency and Code Pipeline Security
Third-party dependencies pinned to verified versions, SAST and SCA run as incremental pipeline checks, license compliance validated at build time, and update workflows maintained so dependency risk is managed actively rather than inherited passively.
Infrastructure Template Review for CI/CD
Terraform, CloudFormation, Kubernetes manifests, and Helm charts scanned for misconfiguration during the build process so infrastructure security is validated at the same stage as application code rather than after provisioning creates the exposure.
Artifact Verification and CI/CD Pipeline Integrity
Software Bill of Materials generated at build time, artifact signatures applied via Sigstore or similar tooling, provenance attestations aligned to SLSA practices and registry promotion policies that reject unsigned or critically vulnerable images.
Risk-Based Gates for a Secure CI/CD Pipeline
Security validation integrated as fast, incremental pipeline checks with risk-calibrated pass/fail thresholds, structured exception processes for approved bypasses, and automated rollback when gate failures reach production through approved channels.
Telemetry for Securing CI/CD Pipeline Behavior
CI/CD event streaming to SIEM with use-case-driven alerting for abnormal build patterns, unexpected privilege use and dependency tampering attempts so behavioral anomalies are detected rather than only signature-matched threats.
Recovery Readiness for CI/CD Application Security
Immutable build logs with tamper-evident storage, registry backup and restore procedures for known-good image catalogs, and documented recovery sequences for the pipeline compromise scenarios most likely to affect your delivery environment.
CI/CD Security That Matches Your Release Pace
Pipeline security that slows down releases does not stay in place. Teams route around controls that create friction. CyberZEALS designs CI/CD pipeline security that runs within your delivery cadence security checks as fast as your builds, gates as light as your risk tolerance allows, and monitoring that runs passively rather than blocking every deployment for manual review.
What You Receive From a CI/CD Security Engagement
01
Pipeline Risk Report
Current gaps and pipeline threat model.
02
Reference Architecture Templates
Secure repo, runner, and policy setup.
03
Build Security Configuration
OIDC runner isolation and log controls.
04
Security Gate Guide
SAST, DAST, SCA, and IaC tuning.
05
Artifact Signing Setup
SBOM provenance and registry enforcement.
Four Outcomes That Pipeline Security Delivers
Verifiable Releases
Signed artifacts with clear build history.
Lower Risk Same Speed
Fast security gates without release delays.
Fewer Pipeline Incidents
Secrets, tampering, and dependency risks reduced.
Stronger Audit Confidence
Clear evidence from commit to deployment.
CI/CD Security Results
Short clean and fits the right-side outcome points.
How CyberZEALS identified critical authorization, file access, request integrity, and account security weaknesses in a private customer portal supporting three
Every Payment Decision, Tested. An authorized manual penetration test of a customer-facing invoice payment application supporting post-payment and prepayment workflows
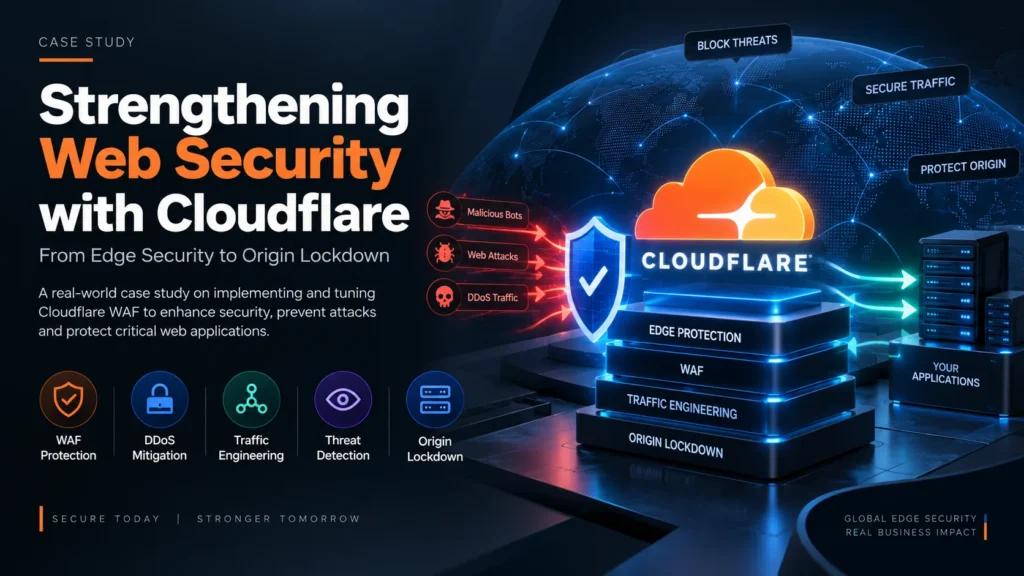
From Edge Security to Origin Lockdown An organization-wide Cloudflare security enhancement combining DNS proxying, TLS hardening, managed and custom WAF
1. Client Background The client is a growing professional services firm that handles sensitive customer data and relies on digital
Five Areas That Make Up a Secure CI/CD Pipeline Program
Repository and CI/CD Pipeline Access Controls
Branch protection rules that require signed commits and approved reviews before merging. Pre-commit hooks and server-side scanning to catch secrets before they enter repository history. Dependency pinning and private proxy configurations that prevent supply chain substitution attacks.
Isolated Build Infrastructure for Secure CI/CD Pipeline
Ephemeral runners that start fresh for each build and are destroyed after, with network egress restricted to approved destinations. Short-lived OIDC credentials rather than stored tokens. Build logs retained with tamper-evident controls that satisfy audit requirements.
Software Supply Chain and Application Security
SBOM generation at build time with continuous vulnerability diffing against your dependency inventory. Artifact signing and attestation using Sigstore or comparable tooling. Registry promotion policies that block unsigned or critically vulnerable images from reaching production registries.
Integrated CI/CD Pipeline Security Testing Gates
SAST, DAST, and API testing as fast incremental checks that run within your existing build stages. SCA with exploit-aware prioritization so high-risk dependency findings are separated from informational ones. IaC scanning with open policy agent integration for policy-as-code enforcement.
Deployment Safety After Securing CI/CD Pipeline
Progressive delivery patterns with automated rollback conditions defined before release rather than decided under pressure during an incident. Change approval workflows mapped to the risk level of each deployment. Kubernetes admission controls and runtime policies that enforce the security posture your pipeline was designed to produce.
How We Secure Your CI/CD Pipeline
We review your existing CI/CD workflows, development processes, security controls, and deployment practices to understand potential risks. This helps identify areas where security improvements can strengthen your software delivery process.
We incorporate security practices into your pipeline to help identify vulnerabilities during development and deployment stages. This enables teams to detect issues earlier without slowing down delivery workflows.
We implement automated security testing and validation processes to improve consistency across your development pipeline. This helps maintain secure deployments while supporting faster and more reliable software releases.
We analyze pipeline performance, review security findings, and refine protection measures as development processes evolve. This helps maintain a secure CI/CD environment throughout the software delivery lifecycle.
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us tighten access and security controls across our CI/CD pipeline without slowing down releases.
DevOps Manager
⭐⭐⭐⭐ 5.0/5
The team identified gaps in our build runners and credentials that we had not fully accounted for.
Platform Engineering Lead
⭐⭐⭐⭐ 5.0/5
Our security gates are now much clearer and easier for developers to work with during deployments.
Release Manager
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us improve secrets handling and reduce unnecessary access across our delivery pipeline.
Cloud Engineering Manager
⭐⭐⭐⭐ 5.0/5
The artifact signing and registry controls gave us better confidence in what was moving into production.
Software Delivery Lead
⭐⭐⭐⭐ 5.0/5
We now have better visibility into pipeline activity and clearer steps for responding when something looks unusual.
Engineering Operations Manager
We are dedicated to transforming businesses through innovative and future migration, storage We are dedicated to transforming businesses.
FREQUENTLY ASKED QUESTIONS
CI/CD Pipeline Security Questions Businesses Ask Before Starting
What is CI/CD pipeline security?
CI/CD pipeline security involves protecting automated software development and deployment processes from security risks.
Why do businesses need CI/CD pipeline security?
Businesses need CI/CD pipeline security to reduce risks during software delivery and ensure secure application deployments.
What does CyberZEALS provide through CI/CD pipeline security services?
CyberZEALS helps businesses improve pipeline security by identifying risks and implementing security practices within development workflows.
How does CI/CD security protect software delivery processes?
CI/CD security helps identify vulnerabilities in deployment workflows and supports safer, more reliable software releases.
Can CyberZEALS secure existing CI/CD environments?
Yes, CyberZEALS helps businesses review and improve existing CI/CD processes to strengthen security throughout deployments.
Who can benefit from CI/CD pipeline security services?
Businesses that use automated software development and deployment processes can benefit from stronger CI/CD security practices.
Recent articles and News
from our blog
As cyber threats become more sophisticated and technology environments grow more complex, organizations need faster and more effective ways to
A new PHP Security Alert deserves attention from anyone responsible for a website, web application, or internet-facing server that runs
Moving workloads, applications, and data to the cloud requires more than simply transferring existing systems to a new environment. Businesses
Some security weaknesses are difficult to understand by looking only at what is visible from the outside. Problems may exist
Certain security threats only become visible when a user logs in, which presents a major issue for security businesses thinking
Security testing approaches may change based on how much information the tester receives before beginning the test. Black Box Penetration
Share a few details about your needs, and we’ll connect you with the right specialist who can guide you on the next steps within one business day.