DevSecOps Managed Services in the USA That Ship Secure Software
Security added at the end of a development cycle finds problems at the most expensive point to fix them. CyberZEALS provides DevSecOps services across the USA that integrate security into every stage of your software pipeline so vulnerabilities are caught when they cost least to address and delivery schedules stay intact.
980+
Successful Services
10+
Years of Experience
900+
Satisfied Clients
10+
Industries Served
DevSecOps Services and Solutions We Deliver
Two foundational programs that run inside your development environment and protect every layer of what your team ships.
Source Code Security Validation
Static analysis, dependency scanning, and secrets detection applied to your codebase during development so security issues are caught at the commit level rather than discovered in a post-deployment audit that triggers a release rollback.
Pipeline Security From Build to Deploy
Infrastructure-as-code scanning, container image hardening, runtime policy enforcement, and delivery gate controls that validate security at every transition in your CI/CD pipeline before code reaches production.
DevSecOps Consulting Services That Change How Security Fits Into Development
Development teams and security teams have historically operated against each other’s timelines. Development pushes for faster releases. Security pushes for more review time. DevSecOps consulting services resolve that conflict not by compromise but by redesigning how security works within the development process. When security testing is automated and integrated into the pipeline, it stops being the bottleneck that delays releases and starts being the verification step that allows faster releases with greater confidence.
DevSecOps Managed Services That Run Continuously in Your Pipeline
Most organizations implement DevSecOps once and then let the program drift as the development environment changes around it. New tools get added. The team structure shifts. Deployment frequency increases. Our DevSecOps managed services keep pace with those changes by actively maintaining the security controls, toolchain configurations, and policy enforcement that keep your pipeline protected as it evolves rather than secured at one point in time and gradually unwound afterward.
Organizations connecting DevSecOps with application security testing and cloud security see the compound benefit pipeline security prevents vulnerabilities from shipping, and application security testing validates the ones that made it through anyway.
Need Reliable IT Support in the USA
Security vulnerabilities found in production cost between 6 and 30 times more to fix than the same issue caught during development. If your team is still treating security as a final-stage gate rather than a continuous pipeline function, CyberZEALS can show you what changing that looks like in practice.
Three DevSecOps Service Offerings That Cover Every Stage
Pipeline Architecture and Toolchain Design
Security toolchain selection, pipeline architecture review, and AWS DevSecOps services configuration that maps your specific technology stack to a security program that fits how your team already works rather than requiring them to change their entire workflow around a new security approach.
Hands-On DevSecOps Implementation in USA
SAST, DAST, SCA, IaC scanning, and secrets detection tools deployed within your actual pipeline, configured for your codebase, and validated to produce actionable findings rather than alert volume your team learns to ignore.
Continuous DevSecOps Managed Services in USA
Ongoing monitoring of your pipeline security controls, rapid response when scan results identify critical findings, and quarterly reviews that keep your DevSecOps program aligned with how your development environment and team structure actually change over time.
Every Payment Decision, Tested. An authorized manual penetration test of a customer-facing invoice payment application supporting post-payment and prepayment workflows
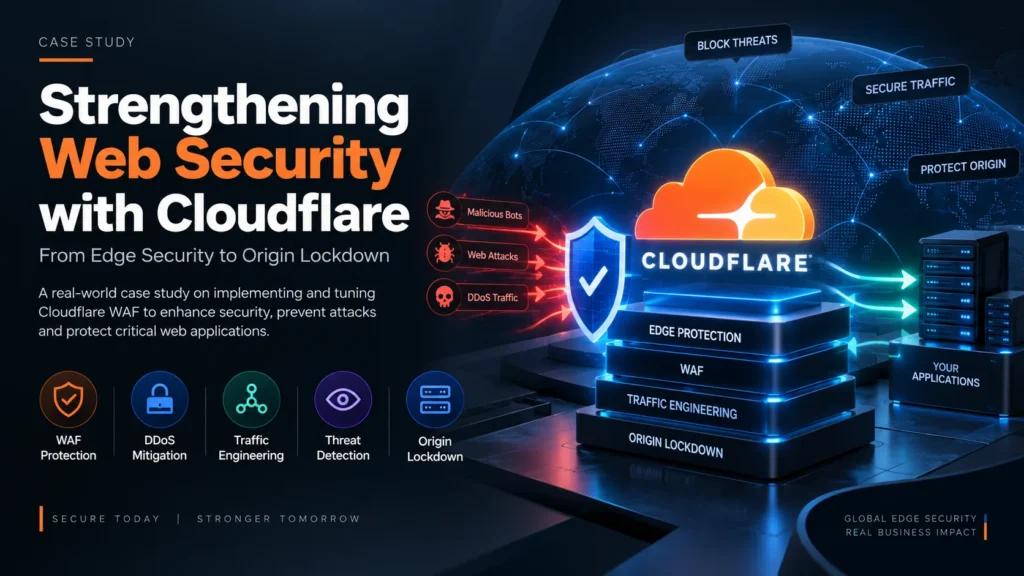
From Edge Security to Origin Lockdown An organization-wide Cloudflare security enhancement combining DNS proxying, TLS hardening, managed and custom WAF
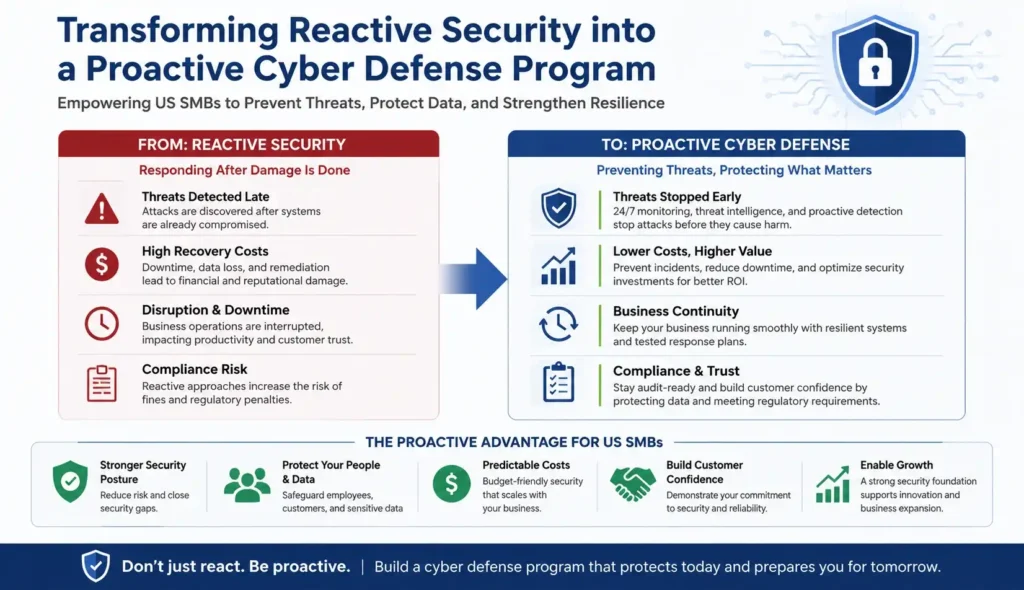
1. Client Background The client is a growing professional services firm that handles sensitive customer data and relies on digital
What Separates Effective DevSecOps Providers From the Rest
Most DevSecOps programs fail not because the tools are wrong but because nobody takes ownership of running them. Scan results pile up without triage. Policy exceptions accumulate without review. The pipeline gets faster and the security program stays where it was. Effective DevSecOps providers take operational responsibility for the program maintaining it, tuning it, and acting on what it produces.
Cybersecurity Service and DevSecOps Integrated
Static code analysis and software composition analysis run at the source level, catching vulnerabilities and license risks in the dependencies your application depends on before those dependencies become production attack surfaces.
DevSecOps as a Service Earlier Detection
Dynamic testing and infrastructure-as-code scanning integrated into your build pipeline so security validation happens at the build stage rather than after a deployment that would require rollback to remediate.
Automated Development Service Security
Security tests, approval gates, and policy enforcement running automatically so your development service delivery maintains speed while security coverage runs in parallel rather than creating the manual review bottleneck that teams eventually route around.
How We Integrate Security Into Your Development Lifecycle
We review your existing development processes, security practices, application workflows, and operational requirements to understand your current DevSecOps maturity. This helps identify opportunities to integrate security more effectively throughout the development lifecycle.
We define security practices that align with your development goals, application requirements, and operational needs. Our approach helps establish secure workflows, automation opportunities, and better collaboration between development and security teams.
We integrate security testing, monitoring, and validation practices into development pipelines to help identify issues earlier. This supports faster delivery while maintaining stronger security throughout the software lifecycle.
We review performance, security findings, and workflow improvements to refine your DevSecOps approach over time. This helps maintain efficient development processes while supporting secure and reliable applications.
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us integrate security checks into our development workflow instead of leaving everything until the end. The code scanning and pipeline controls fit into the way our team was already releasing software.
VP of Engineering
⭐⭐⭐⭐ 5.0/5
We needed better security across our CI/CD pipeline without creating another bottleneck for developers. Their team helped us set up scanning, security gates, and checks that gave us clearer visibility during each release.
DevOps Manager
⭐⭐⭐⭐ 5.0/5
The DevSecOps implementation gave us a more structured way to catch code, dependency, and configuration issues earlier. Findings were easier to prioritize because the security controls were built into the development process.
Application Security Manager
⭐⭐⭐⭐ 5.0/5
We use CyberZEALS for ongoing DevSecOps support as our pipeline and toolchain continue to change. Their team helps keep the security controls maintained and makes sure new changes do not weaken the process.
Director of Technology
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us improve security across the build and deployment process without forcing the development team to change how they work. The added checks gave us more confidence before code moved into production.
Software Engineering Manager
⭐⭐⭐⭐ 5.0/5
The team helped us strengthen areas such as dependency scanning, infrastructure-as-code checks, and secrets detection. The implementation was practical and made it easier to address security issues earlier in the pipeline.
DevSecOps Lead
We are dedicated to transforming businesses through innovative and future migration, storage We are dedicated to transforming businesses.
FREQUENTLY ASKED QUESTIONS
DevSecOps Questions Businesses Ask Before Getting Started
What is DevSecOps?
DevSecOps integrates security practices into the software development lifecycle to help teams build and deliver more secure applications.
Why do businesses need DevSecOps services?
Businesses use DevSecOps to identify security issues earlier, improve development processes, and create more secure software.
What does CyberZEALS provide through DevSecOps services?
CyberZEALS helps businesses integrate security practices into development workflows and improve software delivery processes.
How does DevSecOps improve software development?
DevSecOps helps development and security teams work together to identify risks earlier and improve application security.
Can CyberZEALS help implement security into existing development processes?
Yes, CyberZEALS helps businesses improve existing workflows by adding security practices throughout the development lifecycle.
Who can benefit from DevSecOps services?
Businesses that develop software and want to improve security throughout their development process can benefit from DevSecOps.
Recent articles and News
from our blog
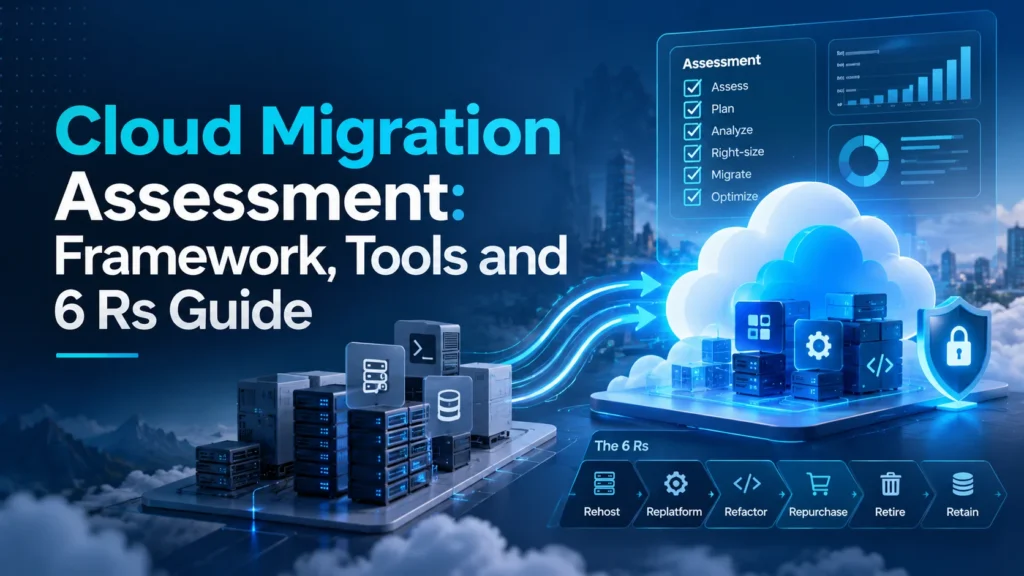
Moving workloads, applications, and data to the cloud requires more than simply transferring existing systems to a new environment. Businesses
Some security weaknesses are difficult to understand by looking only at what is visible from the outside. Problems may exist
Certain security threats only become visible when a user logs in, which presents a major issue for security businesses thinking
Security testing approaches may change based on how much information the tester receives before beginning the test. Black Box Penetration
Penetration testing helps organizations understand their security weaknesses, and the types of penetration testing in cybersecurity determine how different systems
If you are researching SOAR vs MSSP, you are likely trying to strengthen detection and response without overbuilding your security
Share a few details about your needs, and we’ll connect you with the right specialist who can guide you on the next steps within one business day.