Application Security Services in the USA That Protect Your Apps
Application vulnerabilities are the leading attack vector for modern businesses. A single unpatched flaw in a web application, mobile app, or API can expose customer data, disrupt operations, and create compliance exposure that takes months to remediate. CyberZEALS delivers application security services across the USA that identify and close those vulnerabilities before attackers find them.
980+
Successful Services
10+
Years of Experience
900+
Satisfied Clients
10+
Industries Served
Application Security as a Service That Covers the Full Software Lifecycle
The most common application security mistake is treating security as a pre-launch activity. Vulnerabilities introduced during development, missed during testing, and left unmonitored after deployment accumulate into a risk profile that grows with every release cycle. Application security as a service addresses all three phases integrating controls during development, validating them before deployment, and monitoring them continuously after launch so your application security posture does not degrade between annual security reviews.
Why Application Security Managed Services Belong in Every Release Cycle
Applications are the most targeted layer in modern IT environments because they are publicly accessible, frequently updated, and often built under time pressure that compresses security review. Application security managed services that run alongside your development process catch vulnerabilities in the phase where they are cheapest to fix, not after they have been running in production.
- Stop Attacks Before They Reach Users
- Protect Data Across Every Device
- Meet Your Compliance Obligations
Eight Application Security Technology Services We Deploy
Our application security technology services help identify vulnerabilities, strengthen software defenses, and protect business applications from development to deployment.
Security Built Into Your Dev Pipeline
Security requirements defined and validated within your development workflow so vulnerabilities are identified at the code level before they reach a build that will eventually run in production.
Adversarial Testing Before Launch
Manual penetration testing that simulates how an attacker actually engages your application, including authentication attacks, privilege escalation attempts, and business logic abuse that automated scanning consistently misses.
Cloud Application WAF and Rule Management
Web application firewall deployment and ongoing rule tuning for cloud-hosted applications so protection matches how your application is actually used rather than reflecting the vendor defaults that shipped with the tool.
API Security Consulting and Controls
Authentication, authorization, input validation, and rate limiting applied to REST, SOAP, and GraphQL APIs that connect your applications to each other and to the outside world where abuse is most likely to occur.
iOS and Android Security Testing
Static and dynamic testing of mobile applications covering insecure data storage, network communication weaknesses, code tampering exposure, and the device-level vulnerabilities that desktop application testing does not address.
Operational Security Live App Scanning
Continuous scanning of applications in their running state identifies vulnerabilities that only appear when the application is active and processing real traffic the conditions that static code analysis cannot replicate.
Runtime Threat Interception
Security controls embedded within the application itself that detect and block attack attempts at runtime, providing a defense layer that operates even when network perimeter controls have already been bypassed.
Third-Party Dependency Risk Review
Analysis of open-source libraries and third-party components in your application stack so you know which dependencies carry known vulnerabilities before those vulnerabilities are exploited in your production environment.
Application Security Across Every Deployment Stage
Security testing run once before launch and never revisited leaves every subsequent release cycle introducing vulnerabilities without any verification that they were caught. CyberZEALS delivers application security services that run continuously alongside your development process so security coverage keeps pace with your release cadence rather than falling further behind with every deployment.
Application Security Deliverables
01
Vulnerability Risk Report
Ranked application risks with CVSS scoring.
02
Penetration Test Findings
Manual test results with proof and fixes.
03
Secure SDLC Playbook
Coding standards for safer development.
04
WAF Policy Documentation
Configured protection rules for your apps.
05
API and Mobile Test Results
OWASP-based findings with remediation steps.
Application Security Process
Assessment and Threat Modeling
Map applications and identify key risks.
Dev Workflow Security Integration
Add SAST, SCA, and review gates.
Manual Attack Simulation
Test real attack paths and logic flaws.
Remediation and Validation
Fix issues and confirm risk closure.
Runtime Monitoring Coverage
Track security posture after deployment.
Every Payment Decision, Tested. An authorized manual penetration test of a customer-facing invoice payment application supporting post-payment and prepayment workflows
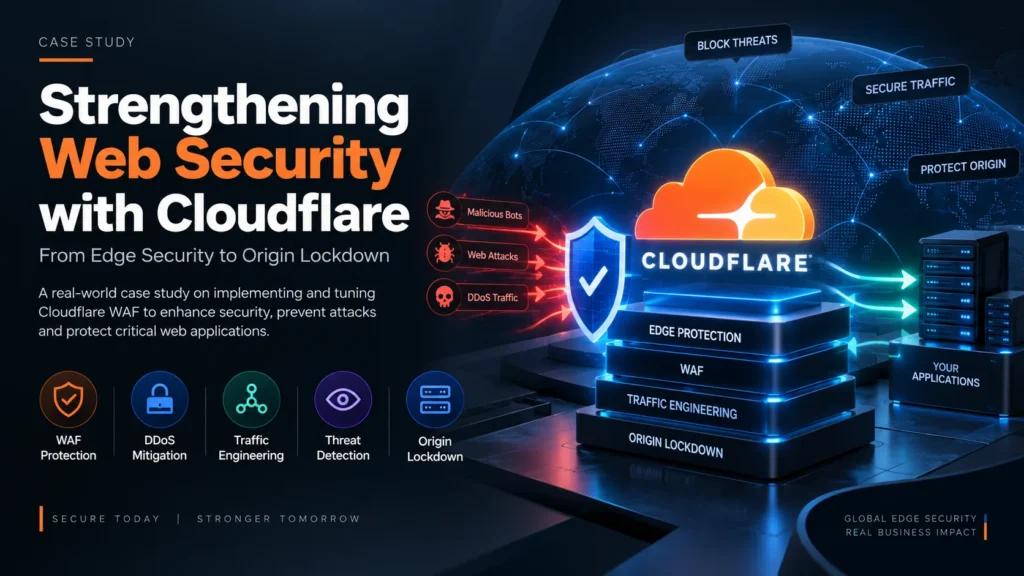
From Edge Security to Origin Lockdown An organization-wide Cloudflare security enhancement combining DNS proxying, TLS hardening, managed and custom WAF
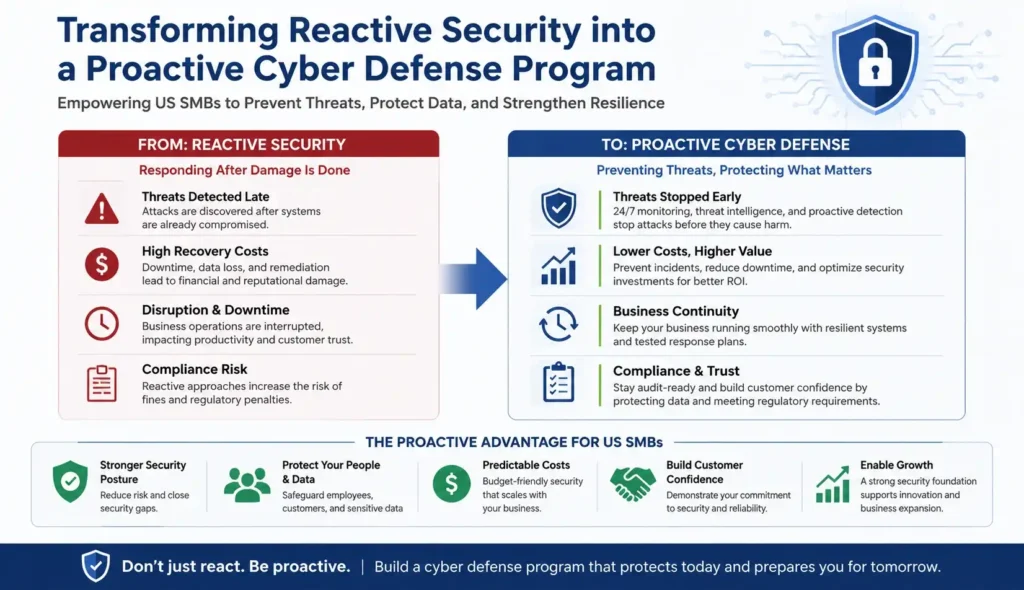
1. Client Background The client is a growing professional services firm that handles sensitive customer data and relies on digital
What Makes CyberZEALS Application Security Services Different
Built Into Development, Not Bolted On
Security requirements defined at the design stage and validated throughout development so your team ships code that was verified secure rather than code that was tested for security after the fact.
Every Attack And Threat Surface Covered
Web applications, mobile applications, APIs, cloud-hosted services, and third-party dependencies all tested under one engagement rather than requiring separate vendors for each application layer.
Testing and Compliance Standards Met
Application security controls and testing procedures mapped to PCI DSS, SOC 2, ISO 27001, and NIST requirements so your applications satisfy compliance auditors, not just internal security reviews.
Findings You Can Act On Immediately
Every vulnerability comes with reproduction steps, business impact context, and specific remediation guidance rather than generic security recommendations that require additional research before your team can act on them.
Security Services That Run Continuously
Application security that does not stop at the pre-launch scan. Runtime monitoring, continuous scanning, and integration into your ongoing release process keep your security posture current rather than point-in-time.
How We Secure Your Applications From Evolving Threats
We review your applications, development practices, security controls, and potential vulnerabilities to understand your current security posture. This helps identify areas where stronger protection and security improvements are needed.
We develop security measures based on your application architecture, business requirements, and risk exposure. Our approach focuses on reducing vulnerabilities and improving the overall security of your applications.
We apply application security controls, testing approaches, and protection measures designed to safeguard applications throughout their lifecycle. This helps improve resilience against potential threats and unauthorized activity.
We review security findings, identify opportunities for improvement, and refine protection strategies as applications evolve. This helps maintain secure and reliable applications over time.
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us improve the security of our applications with a structured approach. Their team provided valuable guidance to identify risks and strengthen our application protection.
Application Security Engineer
⭐⭐⭐⭐ 5.0/5
We needed a better way to address security concerns within our applications. CyberZEALS helped us improve our security practices and build more reliable software environments.
Software Engineering Manager
⭐⭐⭐⭐ 5.0/5
CyberZEALS provided practical support for improving our application security. Their team helped us identify weaknesses and implement better security measures.
DevOps Engineer
⭐⭐⭐⭐ 5.0/5
Protecting our applications became a higher priority as our systems grew. CyberZEALS helped us create a stronger security approach focused on reducing risks.
Technology Lead
⭐⭐⭐⭐ 5.0/5
CyberZEALS helped us improve our application security strategy with expert guidance and support. Their approach made it easier to identify and address security challenges.
Systems Architect
⭐⭐⭐⭐ 5.0/5
We wanted to strengthen the security of our applications and reduce potential risks. CyberZEALS provided the expertise needed to improve our overall application security process.
IT Security Specialist
We are dedicated to transforming businesses through innovative and future migration, storage We are dedicated to transforming businesses.
FREQUENTLY ASKED QUESTIONS
Application Security Questions Businesses Ask Before Getting Started
What is application security?
Application security involves protecting software applications from vulnerabilities, threats, and unauthorized access.
Why do businesses need application security services?
Businesses need application security to protect applications, reduce vulnerabilities, and improve the safety of their software environments.
What does CyberZEALS provide through application security services?
CyberZEALS helps businesses identify application risks and implement security measures to improve application protection.
Can CyberZEALS help secure existing applications?
Yes, CyberZEALS helps businesses evaluate application security and improve protection based on identified risks.
How does application security improve software reliability?
Application security helps identify weaknesses early and supports safer, more reliable software environments.
Who can benefit from application security services?
Businesses that develop, use, or manage applications requiring stronger protection can benefit from application security services.
Recent articles and News
from our blog
Moving workloads, applications, and data to the cloud requires more than simply transferring existing systems to a new environment. Businesses
Some security weaknesses are difficult to understand by looking only at what is visible from the outside. Problems may exist
Certain security threats only become visible when a user logs in, which presents a major issue for security businesses thinking
Security testing approaches may change based on how much information the tester receives before beginning the test. Black Box Penetration
Penetration testing helps organizations understand their security weaknesses, and the types of penetration testing in cybersecurity determine how different systems
If you are researching SOAR vs MSSP, you are likely trying to strengthen detection and response without overbuilding your security
Share a few details about your needs, and we’ll connect you with the right specialist who can guide you on the next steps within one business day.